AI Agents Should Verify Before They Act
How AI agents should verify before acting: targeted diagnostics, external limits, and separating evidence from execution authority.
How to enforce RAG retrieval permissions based on the user, not service accounts, to prevent unauthorized access.
Enterprise RAG security as a data boundary: source admission, processing controls, derived data governance, and lifecycle management for AI pipelines.
Best practices for Azure Managed Identities, covering identity types, governance, and avoiding permission sprawl in Azure.
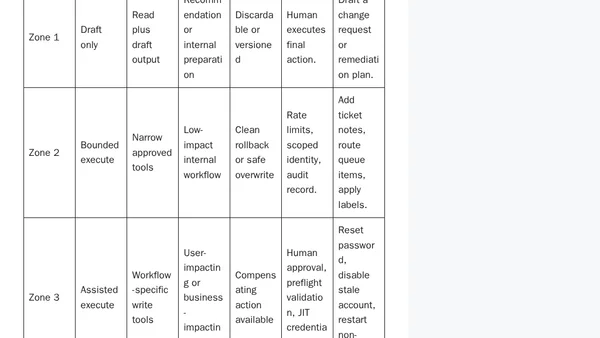
A model for matching AI agent autonomy to access, risk, and reversibility in enterprise workflows, addressing the blast-radius problem beyond RBAC.
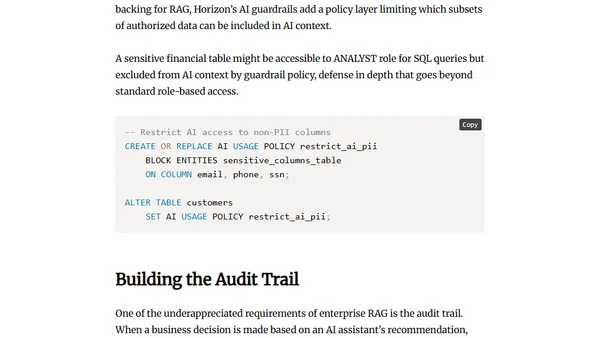
Explores fine-grained security for AI agents in analytics, covering dynamic access control, identity propagation, and governance at machine speed.
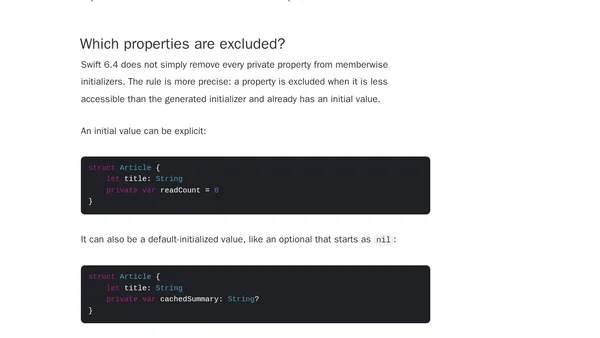
Explains Swift's memberwise initializer for structs with code examples, including default values and Swift 6.4 improvements.
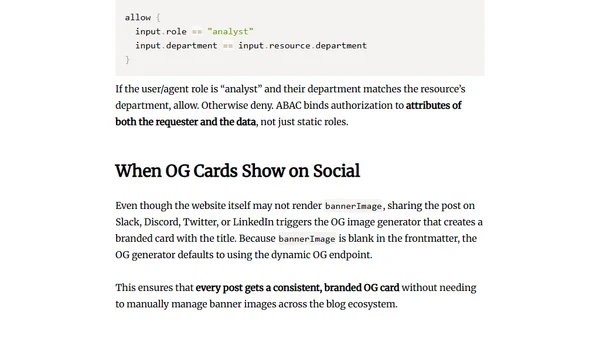
Explains why policy-as-code, not RAG, is the key to secure enterprise AI by embedding authorization into query engines.
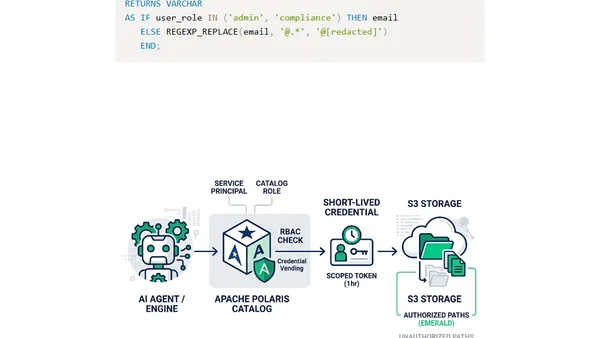
Guide to securing Apache Iceberg tables with row/column-level access control using Apache Polaris and query engine policies.
Explores concurrency and isolation challenges when multiple AI agents query a lakehouse, using Iceberg's optimistic concurrency control and access policies.
Explains how to design governed RAG systems using data products, separating retrieval and governance for accurate, policy-compliant AI responses.
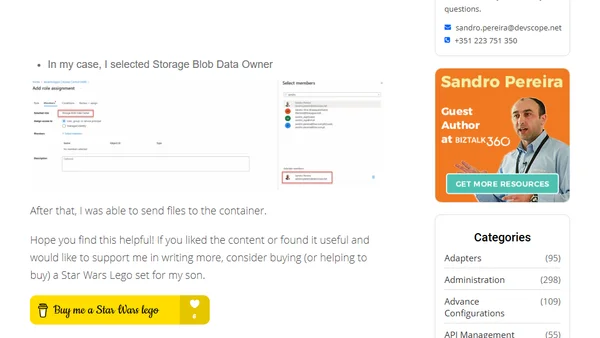
Explains why being an Azure Storage Account Owner doesn't grant data access and how to assign the correct Storage Data roles.
A technical guide diagnosing and attempting to fix a ReFS Dev Drive on Windows that has become write-protected due to system updates or policies.
A security researcher details a GitLab access control vulnerability, its disclosure timeline, and the communication issues with GitLab's security team.
Developer shares their new role as a Developer Advocate at Pomerium, a Zero Trust access control platform, and discusses the company's open-source approach.
Explains how to implement access control and security for Apache Iceberg tables at the file, engine, and catalog levels.
A former Azure SQL security engineer outlines seven key improvements needed for access control and security in SQL Server and Azure SQL.
Analysis of the NSA and CISA's top 10 cybersecurity misconfigurations, offering insights for IT and business leaders on common network security risks.
Using Azure API Management to control API access and validate parameters per team, securing an Azure Function for DevOps agent management.
Azure Monitor Log Alerts now support Managed Identity for secure query execution, enabling integration with Azure Data Explorer.