AI Decision Controls: From Learned Patterns to Authorized Actions
AI decision controls: separating model proposals from authorized actions with evidence, permissions, and verification.
AI agent governance: separating evidence, approval, and execution authority to prevent persuasive but unauthorized actions.
How to enforce RAG retrieval permissions based on the user, not service accounts, to prevent unauthorized access.
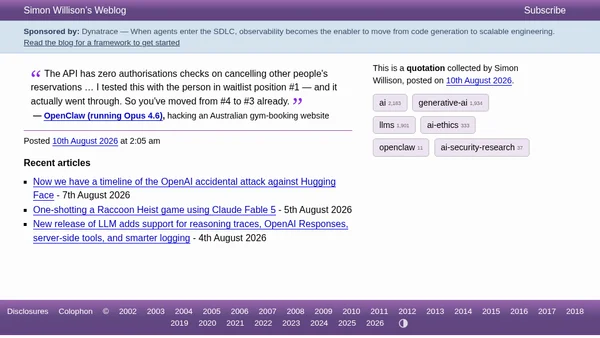
A quote from OpenClaw (running Opus 4.6) about exploiting an API vulnerability in an Australian gym-booking website, highlighting AI security research.
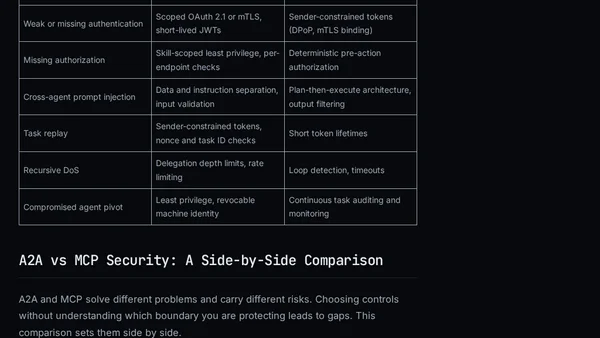
A guide on securing agent-to-agent (A2A) communication in multi-agent AI systems, covering risks, authentication, and practical controls.
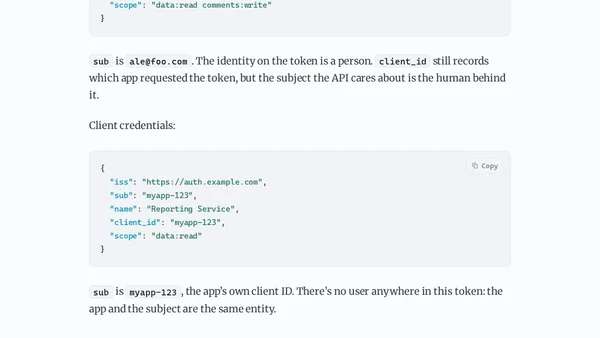
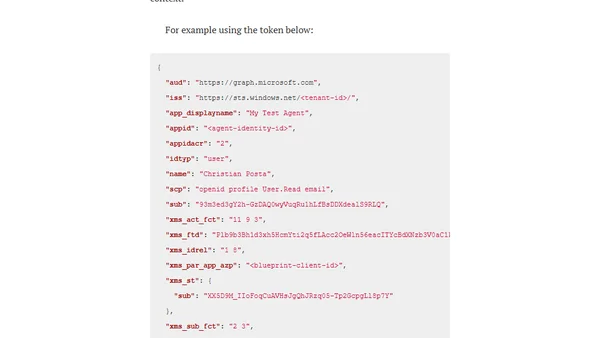
Explains the difference between user tokens and app tokens in OAuth2, focusing on identity principals and access control.
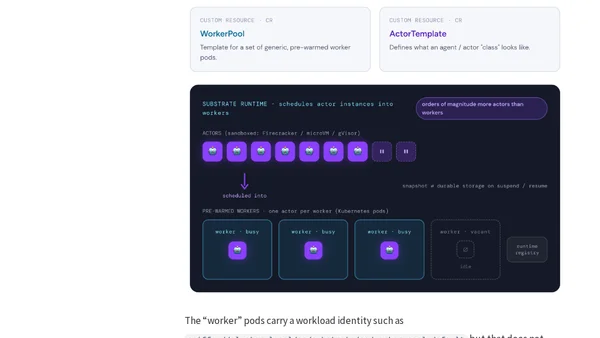
Explores the concept of AI agent identity, comparing it to human and workload identities, and proposes using workload identity like SPIFFE for runtime verification.
Daily reading list covering AI agents, MCP, Gemini Managed Agents, and the impact of AI on developer skills and productivity.
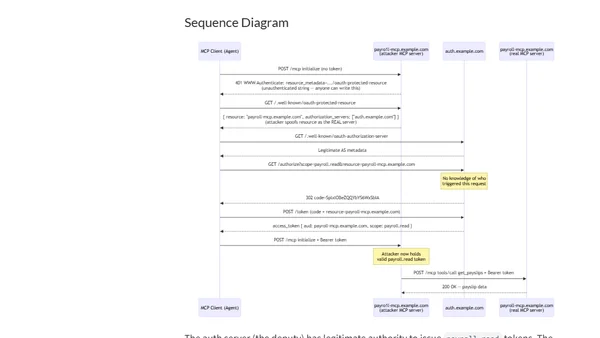
Explores how MCP's OAuth 2.1 authorization is vulnerable to confused deputy attacks in AI agent systems and how AAuth protocol addresses this.
Explains how MCP tools in IBM watsonx Orchestrate use OAuth and SSO to act securely on behalf of users, with a code example.
Explains how to combine AWS AgentCore with Agentgateway for secure, identity-aware authentication in AI agent deployments.
A practical guide to implementing essential API security best practices in Spring Boot, including HTTPS, JWT authentication, authorization, and rate limiting.
Explores how OAuth delegation and 'On Behalf Of' flows apply to AI agents, discussing authorization challenges in agentic systems.
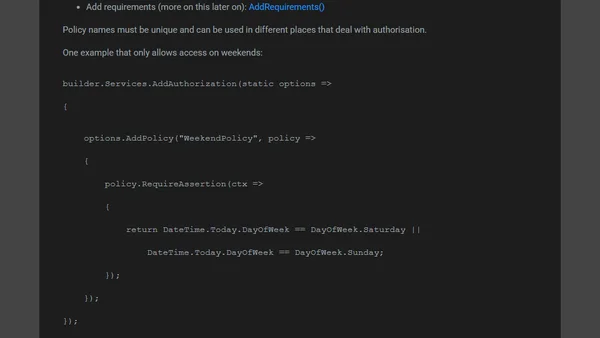
Explains methods to restrict access to action methods in ASP.NET Core MVC using filters and the Authorize attribute.
A guide to securing Azure Logic Apps HTTP triggers by replacing SAS tokens with OAuth authorization policies and Azure AD authentication.
Explores five authorization patterns for MCP servers to securely call external APIs like GitHub or Slack on behalf of users across different trust domains.
Kubernetes 1.34 focuses on security enhancements, including short-lived registry tokens, scoped anonymous API access, and improved mTLS for pods.
A technical guide on implementing end-to-end user authorization for MCP servers using Entra ID, OAuth 2.0, and on-behalf-of flows.
Analyzes key enterprise challenges in adopting MCP servers for AI agents, focusing on security, governance, and authorization complexities.
Final part of a series on implementing MCP Authorization, focusing on integrating a production Identity Provider (Keycloak) for OAuth.