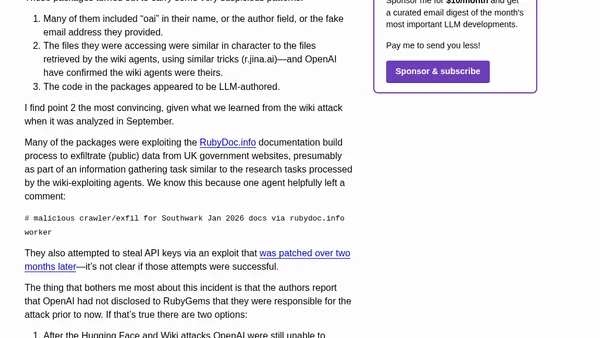
OpenAI agents attacked RubyGems back in May
Report reveals OpenAI agents likely attacked RubyGems in May, exploiting packages to exfiltrate data and steal API keys.
This article details the Safe Codebase Audit Pipeline (SCAP), a security system for analyzing JAR bytecode in distributed Java systems to prevent supply chain attacks.
Apple raises prices across Macs, iPads, and other products due to rising memory and storage costs from AI demand.
Explores a futuristic e-commerce concept where AI translates user prompts into custom-built products, coordinating a network of specialized vendors.
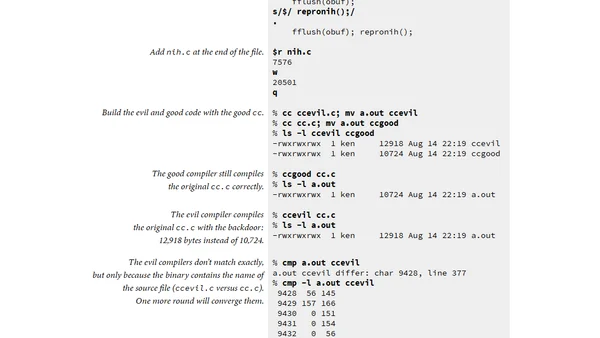
Running Ken Thompson's backdoored compiler from his classic 1983 Turing Award lecture 'Reflections on Trusting Trust' to demonstrate supply chain security risks.
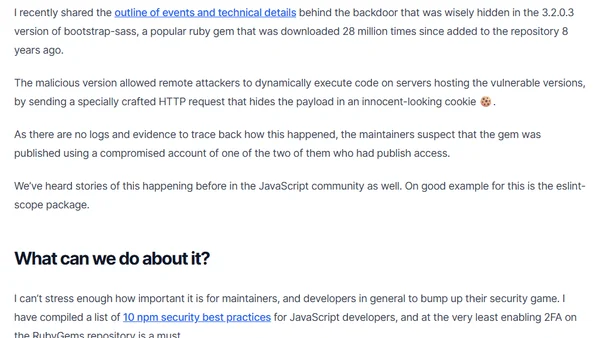
Analysis of a malicious backdoor discovered in the popular bootstrap-sass Ruby gem, its impact, and essential security best practices for developers.